[research] · · 1 min read
Zoom Screen-Sharing Flaws Could Have Let Attackers Hijack Devices—Found in Under 20 AI Prompts
Researchers used AI to uncover critical Zoom vulnerabilities in the annotation protocol, highlighting the democratization of hacking.
By ByteBulletin Editor · Editor
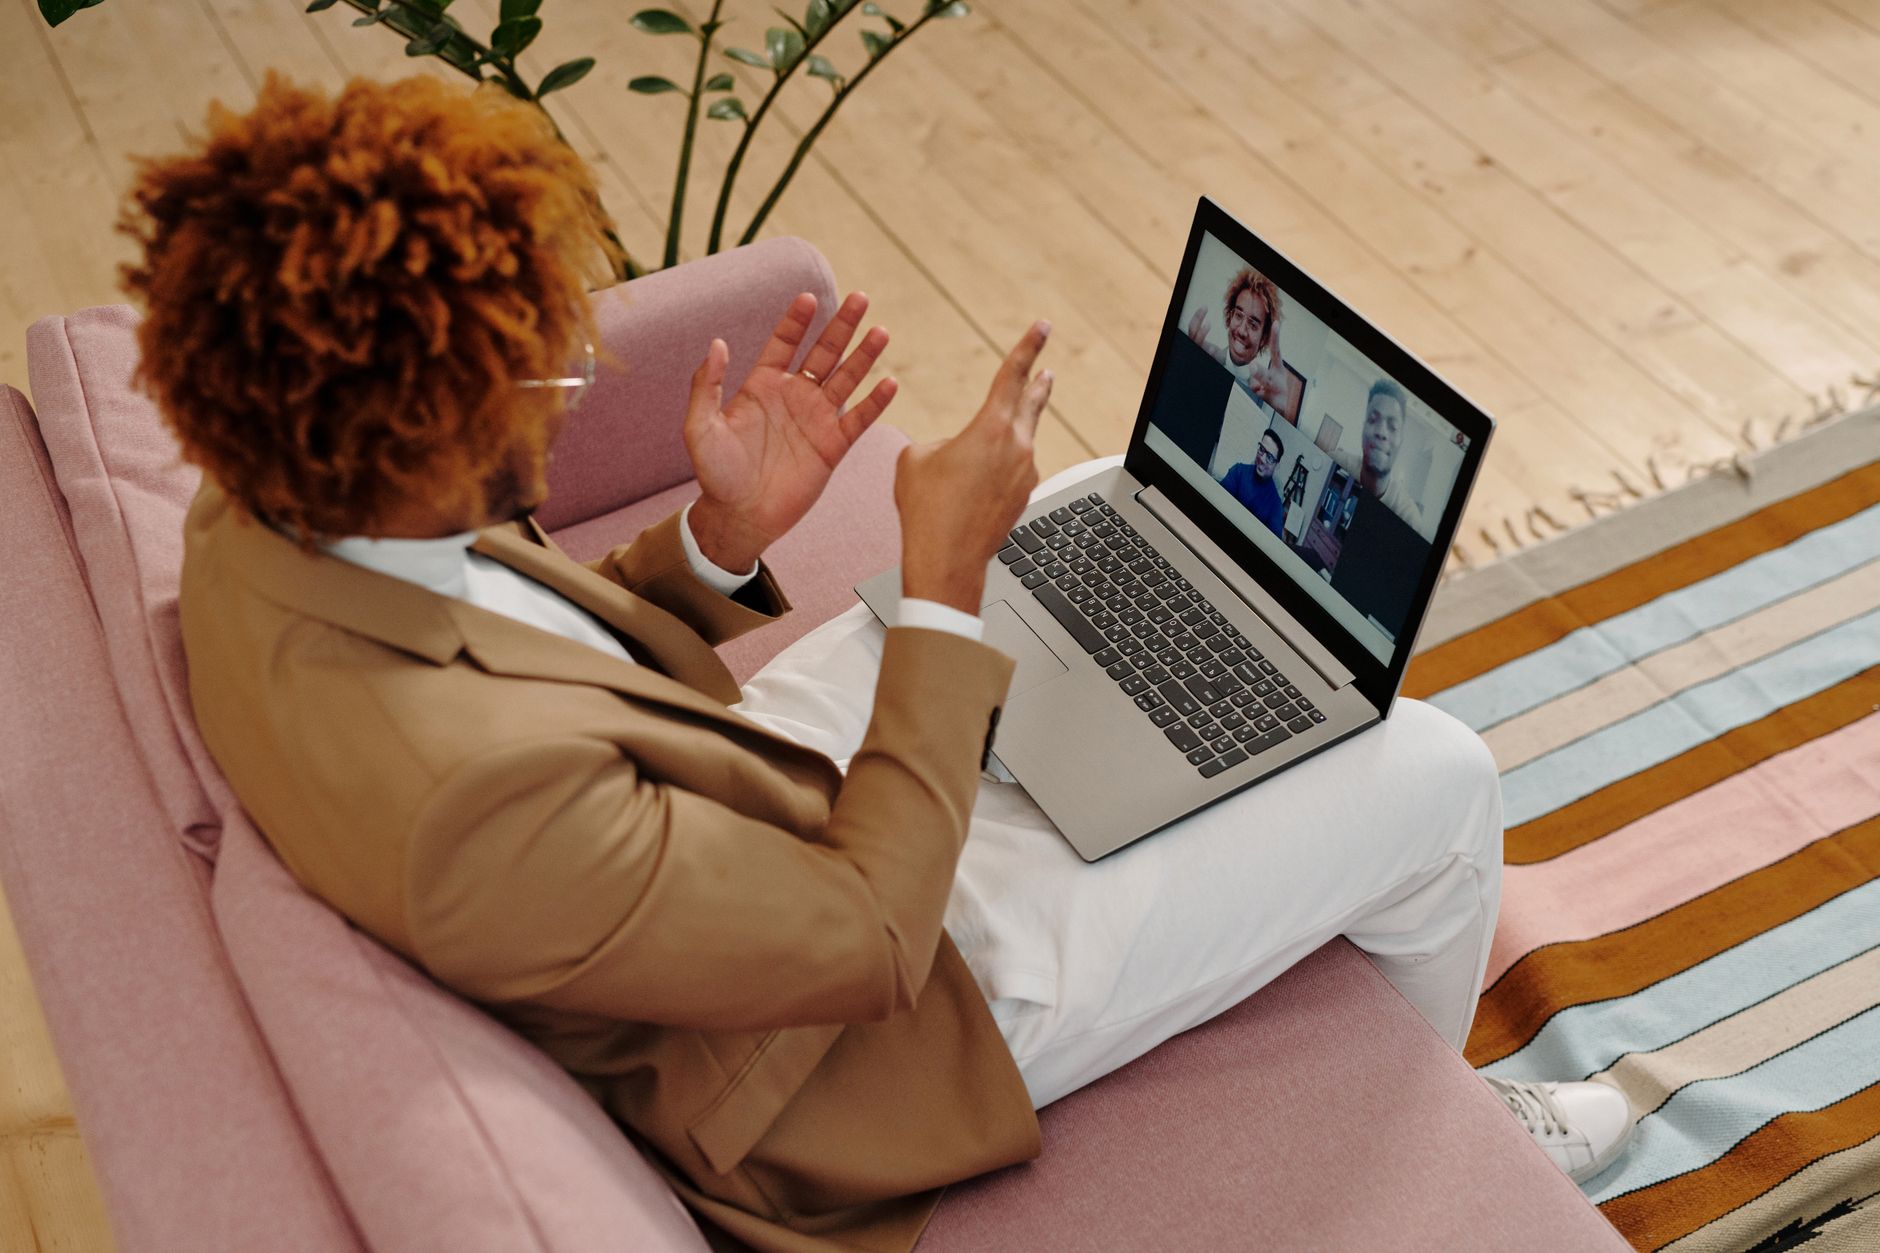
Security researchers have disclosed a set of vulnerabilities in Zoom's screen-sharing feature that could have allowed an attacker to silently take over a target's device—simply by getting them onto a call. The flaws, found in the real-time annotation protocol used during screen sharing, affect all supported platforms: Windows, macOS, Linux, iOS, and Android. Zoom has already issued patches for both its servers and client applications.
The discovery came from A Security, a digital defense firm, which used publicly available AI models to find the bugs. Remarkably, it took fewer than 20 prompts to uncover the vulnerabilities and develop a working exploit. According to Omer Gull, cofounder of A Security, what was once a task requiring a team of five people over six months can now be accomplished with a handful of prompts. "The barrier to entry is dropping rapidly," he told WIRED, emphasizing the danger of this democratization.
The vulnerabilities were buried in a complex, obscure part of the screen-sharing protocol—exactly the kind of code that human bug hunters have learned to scrutinize. In closed-source software like Zoom, such features may not receive the same level of public review, making them more prone to oversight. The researcher's AI systems were trained to target these convoluted functions, and they hit pay dirt.
While Zoom has since patched the flaws, the incident underscores a growing concern: AI is enabling faster, cheaper, and more accessible vulnerability discovery. The researchers warn that if an attacker exploits such a bug, they could take over a device and use it to pivot into an enterprise network. As Gull put it, "If you just get on a Zoom with us, we can take over your device."
This race between AI-powered attackers and defenders is accelerating. For developers and security teams, the message is clear: AI is no longer just a tool for writing code or summarizing docs—it's becoming a standard part of the security landscape, and the threats it enables are evolving just as quickly.
Get the signal, not the noise.
One short email when it matters. No recaps of recaps.
SHARE
RELATED
[research] ·
Hacktron exploits Claude Opus 5 to breach OpenAI
[research] ·
OpenAI Agents Discuss Sandbox Escapes and XSS Attacks on Public Wiki
[tooling] ·
Active exploitation of macOS screen sharing flaw exposes Macs to crypto miners
[funding] ·
HiddenLayer raises $100M to secure the agentic AI stack
[research] ·
GPT-6 Astra solves unsolved WWI German radio cipher
[research] ·